Security

Patient data, protected by default.

Encryption, role-based access, audit logging, and a signed BAA on every plan, for practices that handle PHI every day.
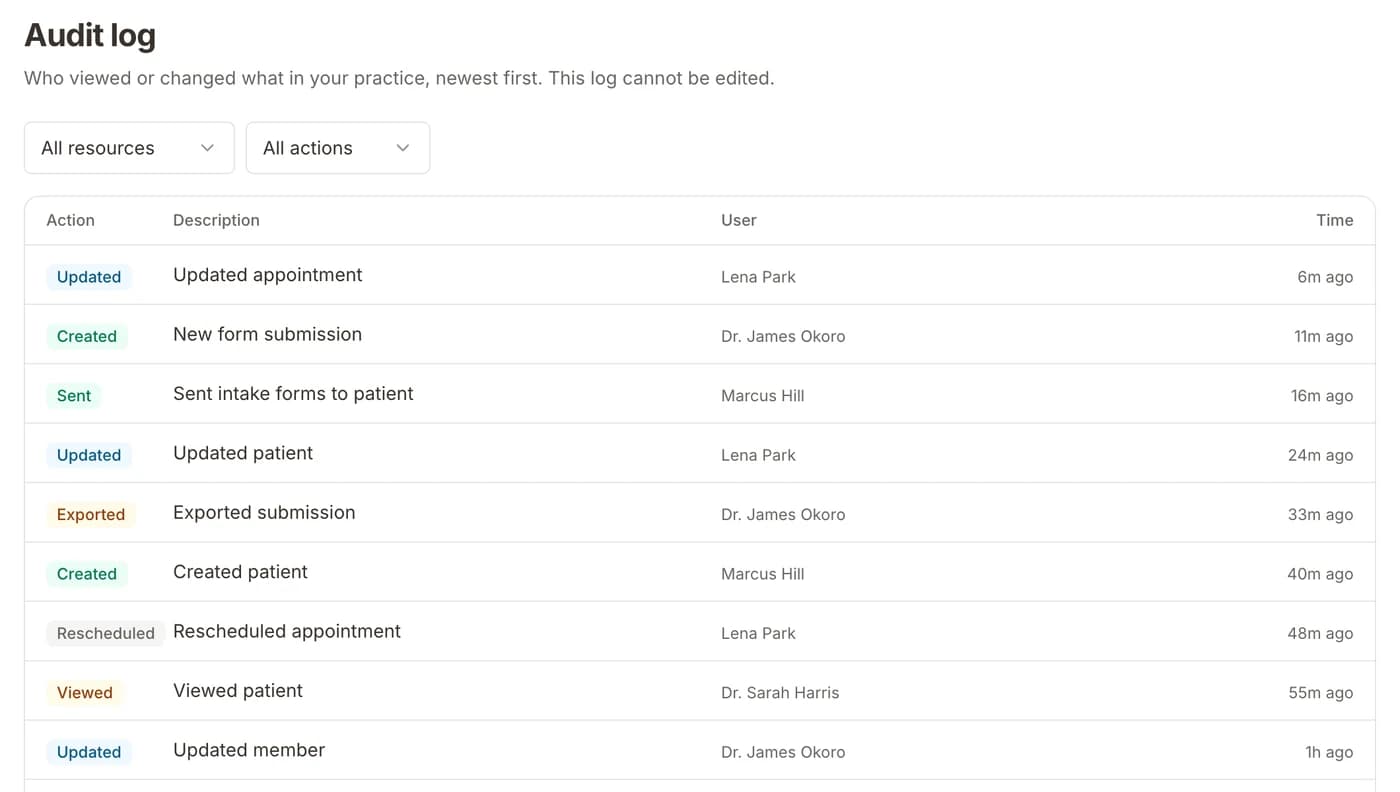
The audit log showing which teammate viewed, created, sent, or exported patient records, and when

Encrypted everywhere

AES-256 on the database and file storage. HTTPS with TLS 1.2 or 1.3 on every connection.

Access by role

Admin, Provider, and Staff roles. Only admins invite teammates, change roles, or see the audit log.

An audit trail

Changes to patients, forms, submissions, and appointments are logged with the user, time, and IP address.

Safeguards

Encryption at rest
AES-256 encryption on the PostgreSQL database, its backups, and file storage for uploads.
Encryption in transit
HTTPS only, with TLS 1.2 as the minimum and TLS 1.3 supported. Database connections require TLS.
US hosting
The application, database, and file storage run on AWS in the United States (us-east-1).
Practice isolation
Every record belongs to one practice, and each request is checked against the user's membership and role.
Uploaded files
Patient uploads are private and served through signed links that expire after an hour.
Passwords and webhooks
Passwords are hashed with bcrypt. Outgoing webhooks are signed with HMAC so you can verify them.
Backups
Automated daily database backups kept for 7 days, with a standby database in a second availability zone.
Monitoring
Account activity is recorded with AWS CloudTrail and watched by Amazon GuardDuty.
Business Associate Agreement
Included on every plan and accepted in Settings under Compliance.

Certified infrastructure

Formisoft runs on ISO 27001 and ISO 27799 certified infrastructure, with HIPAA safeguards on top.

Formisoft runs on ISO 27001 certified infrastructure

ISO 27001

Certified under ISO/IEC 27001:2022. Independently audited annually.

Formisoft runs on ISO 27799 certified infrastructure

ISO 27799

Certified under ISO 27799:2016. Health informatics security management for healthcare organizations.

Formisoft is HIPAA compliant

HIPAA

Administrative, physical, and technical safeguards for all patient health information.

Questions

Formisoft provides the safeguards HIPAA expects from a business associate: a signed BAA on every plan, encryption in transit and at rest, role-based access, audit logging, and US hosting. Your practice stays responsible for how your team uses the product.

The database, its backups, and uploaded files are encrypted at rest with AES-256. Data in transit uses HTTPS with TLS 1.2 or 1.3, and connections to the database require TLS. Passwords are hashed with bcrypt.

Creating, updating, and deleting patients, forms, submissions, and appointments, plus team invites and sensitive reads. Each entry records the user, action, record, time, IP address, and browser. Admins can filter the log in Settings under Compliance.

Admin, Provider, and Staff for your team, plus a Patient role. Admins manage the team, billing, and settings. Only admins can invite members, change roles, or remove members.

Yes. A BAA is included on every plan at no extra cost. It establishes Formisoft as a business associate handling protected health information (PHI) on behalf of your practice.

The application, database, and file storage run on Amazon Web Services in the United States (us-east-1).

Questions about security?

We can walk your compliance officer through how Formisoft handles PHI.

Cancel anytime · BAA included